|
Bearsampp 2026.9.23
|
|
Bearsampp 2026.9.23
|
Static Public Member Functions | |
| static | generateToken () |
| static | getStats () |
| static | getToken () |
| static | getTokenField () |
| static | getTokenMeta () |
| static | init () |
| static | regenerateToken () |
| static | validateOrDie ($removeAfterValidation=false) |
| static | validateRequest ($removeAfterValidation=false) |
| static | validateToken ($token, $removeAfterValidation=false) |
Data Fields | |
| const | MAX_TOKENS = 10 |
| const | SESSION_KEY = 'bearsampp_csrf_tokens' |
| const | TOKEN_EXPIRATION = 7200 |
Static Private Member Functions | |
| static | cleanupExpiredTokens () |
| static | configureSession () |
| static | getAllHeaders () |
| static | getAllowedHosts () |
| static | getOriginPort (array $parts, $scheme) |
| static | getRequestPort ($httpHost, $scheme) |
| static | isAllowedOrigin ($url, $httpHost, $scheme, array $allowedHosts) |
| static | isHostAllowed ($host, array $allowedHosts) |
| static | normalizeHost ($host) |
| static | validateOrigin () |
Class Csrf
Provides CSRF (Cross-Site Request Forgery) protection for the Bearsampp application. This class handles token generation, validation, and management to prevent CSRF attacks.
Features:
Usage:
Definition at line 34 of file class.csrf.php.
|
staticprivate |
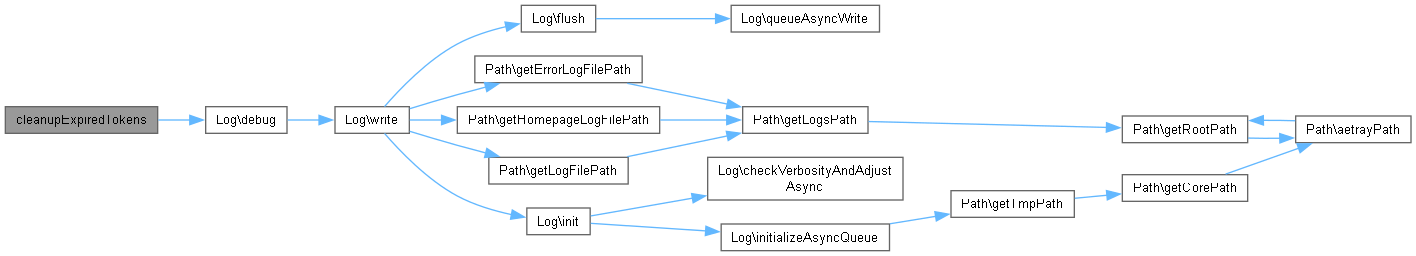
Removes expired tokens from the session.
Definition at line 606 of file class.csrf.php.
References Log\debug().
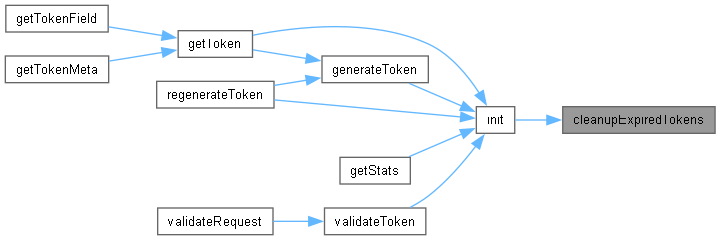
Referenced by init().
|
staticprivate |
Hardens the session configuration before a session is started. These settings are also present in the bundled php.ini, but are applied here as defense in depth in case that file is customized.
Definition at line 84 of file class.csrf.php.
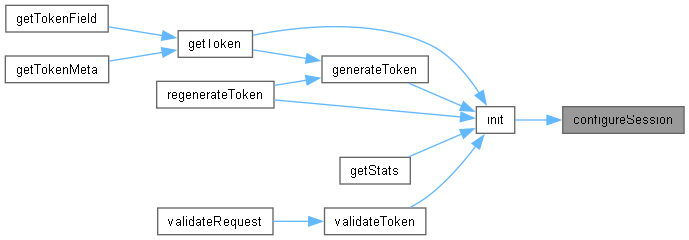
Referenced by init().
|
static |
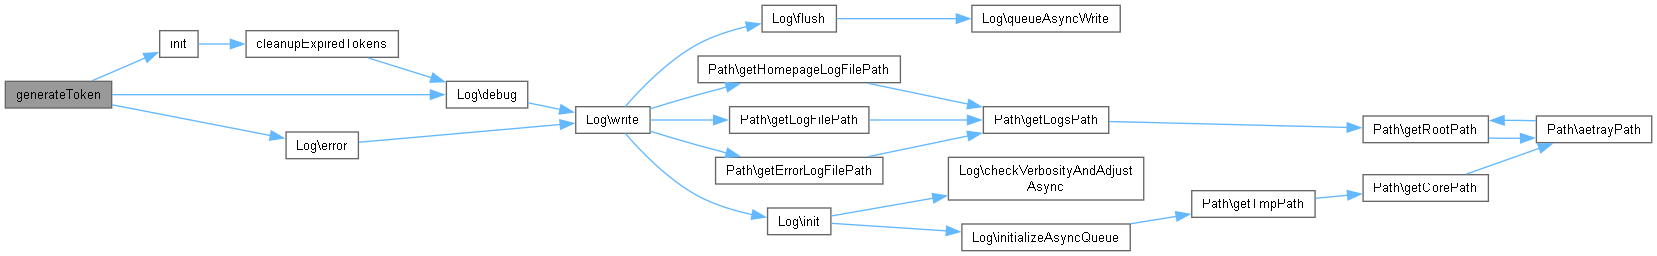
Generates a new CSRF token and stores it in the session.
| Exception | If random_bytes() fails |
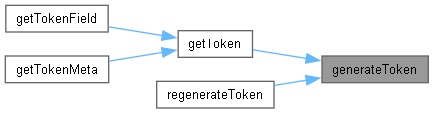
Definition at line 111 of file class.csrf.php.
References Log\debug(), and init().
Referenced by getToken(), and regenerateToken().
|
staticprivate |
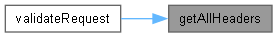
Gets all HTTP headers in a cross-compatible way. Works with both Apache and FastCGI/CGI environments.
Definition at line 573 of file class.csrf.php.
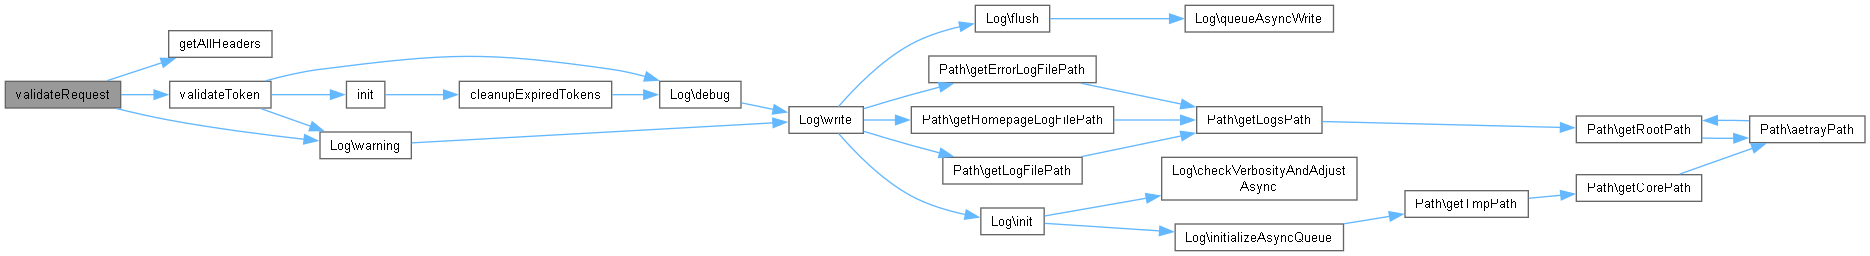
Referenced by validateRequest().
|
staticprivate |
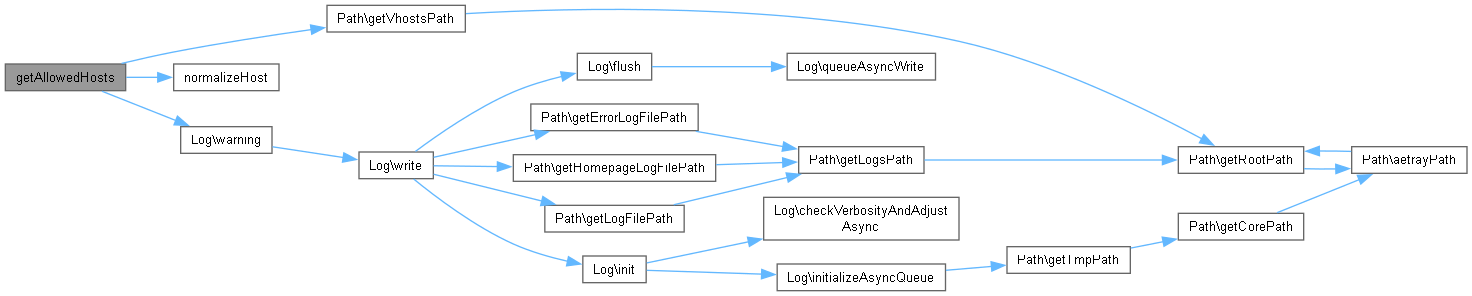
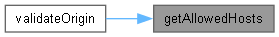
Builds the allowlist of hosts the local server is intended to serve. Keeps DNS-rebinding protection effective while still allowing access through the machine hostname and any user-configured virtual hosts.
Definition at line 311 of file class.csrf.php.
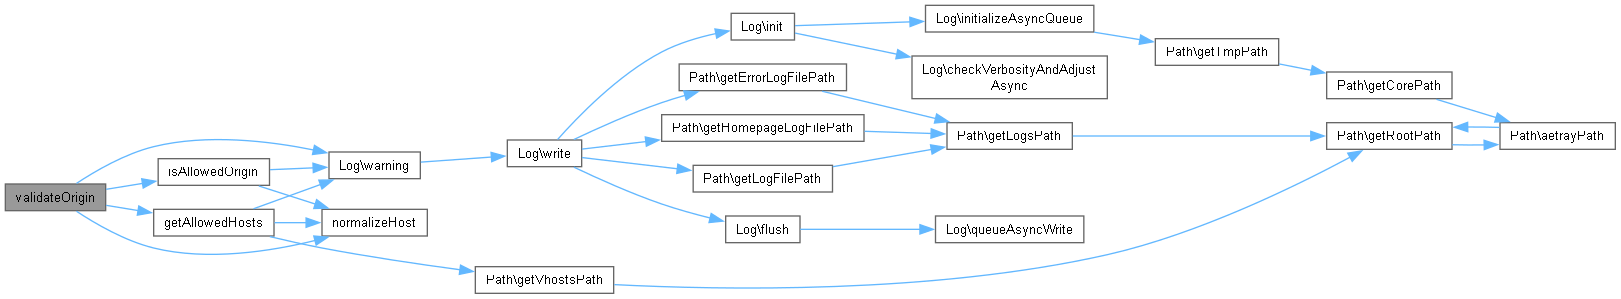
References $bearsamppBins, $bearsamppConfig, APP_LOCALHOST, Path\getVhostsPath(), normalizeHost(), and Log\warning().
Referenced by validateOrigin().
|
staticprivate |
Resolves the effective port of an Origin/Referer URL, falling back to the default port of the scheme when none is explicitly present.
| array | $parts | The parsed URL components. |
| string | $scheme | The origin scheme ('http' or 'https'). |
Definition at line 540 of file class.csrf.php.
|
staticprivate |
Resolves the effective port of the request from the HTTP_HOST header, falling back to the default port of the scheme when none is present.
| string | $httpHost | The raw HTTP_HOST header (may include a port). |
| string | $scheme | The request scheme ('http' or 'https'). |
Definition at line 558 of file class.csrf.php.
|
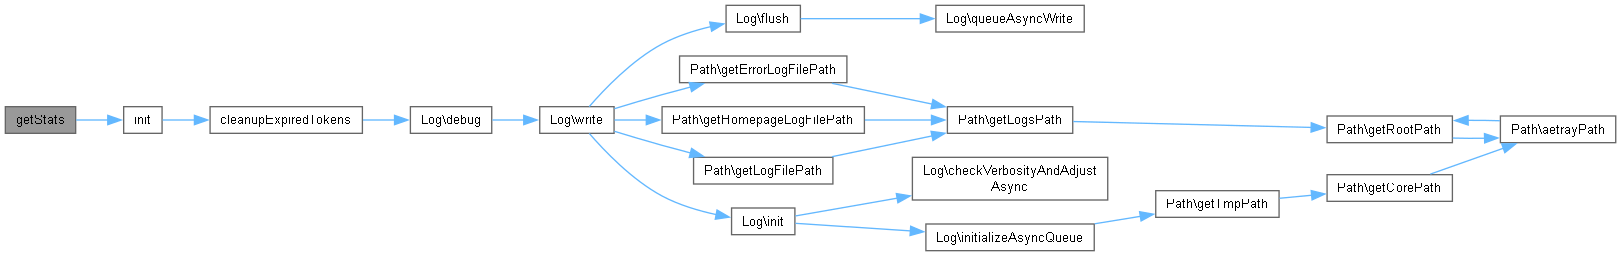
static |
Gets statistics about current CSRF tokens. Useful for debugging and monitoring.
Definition at line 698 of file class.csrf.php.
References init().
|
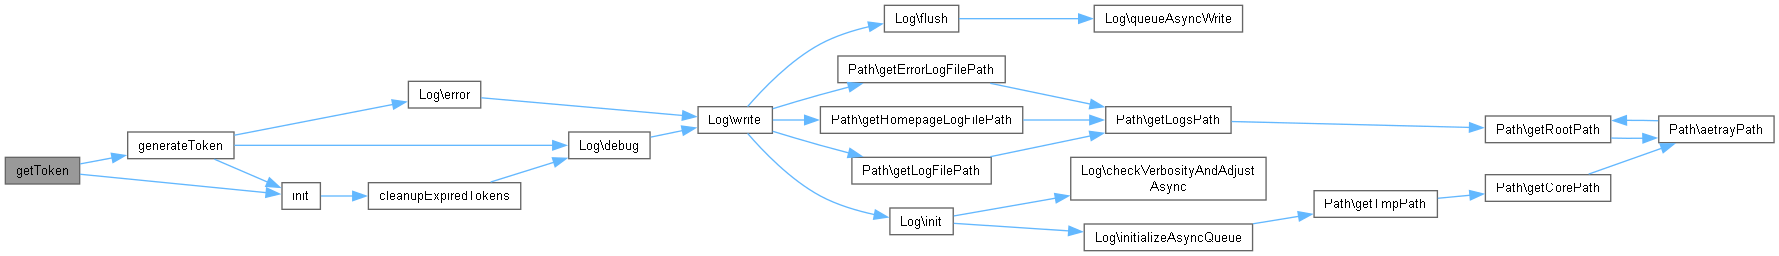
static |
Gets the current CSRF token, generating a new one if none exists.
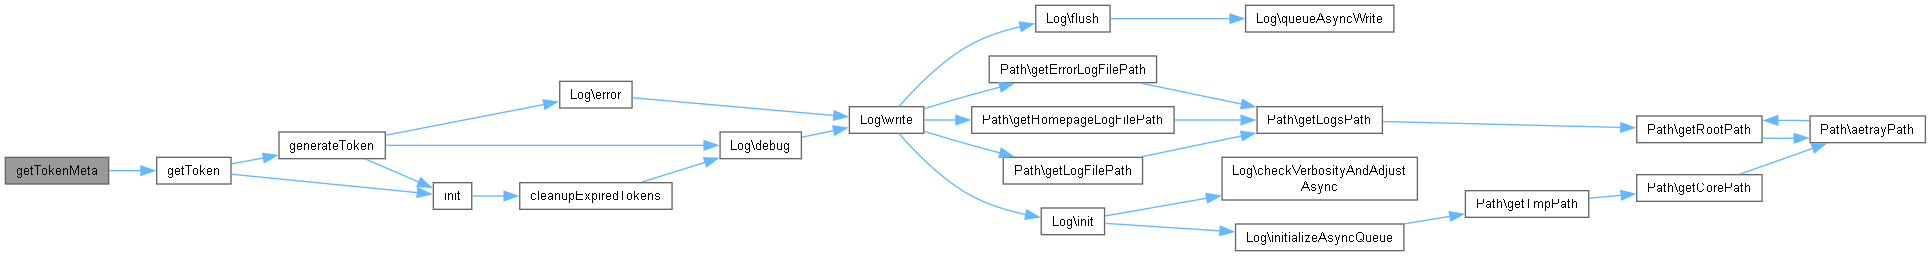
Definition at line 140 of file class.csrf.php.
References generateToken(), and init().
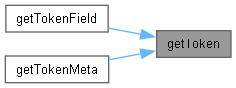
Referenced by getTokenField(), and getTokenMeta().
|
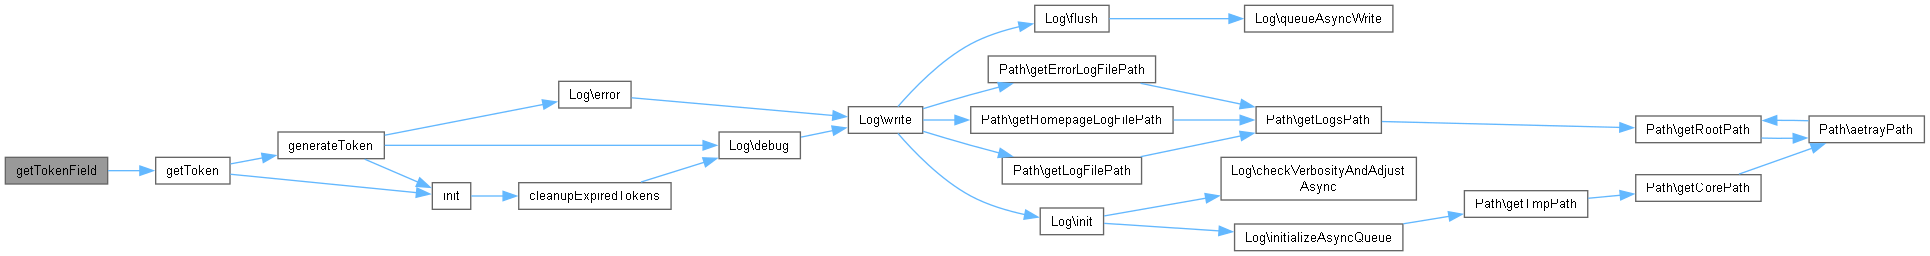
static |
Gets the token as a hidden input field for forms.
Definition at line 651 of file class.csrf.php.
References getToken().
|
static |
Gets the token as a meta tag for inclusion in HTML head. Useful for AJAX requests.
Definition at line 664 of file class.csrf.php.
References getToken().
|
static |
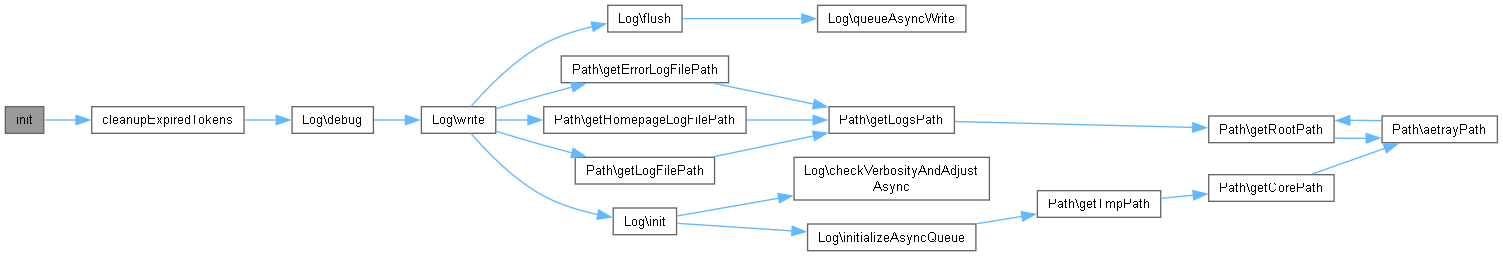
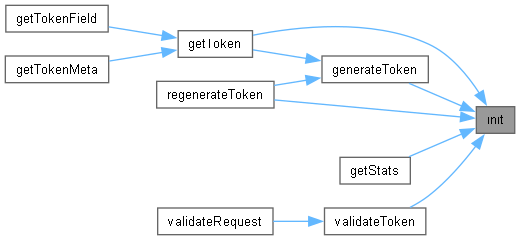
Initializes the CSRF protection system. Starts the session if not already started and cleans up expired tokens.
Definition at line 58 of file class.csrf.php.
References cleanupExpiredTokens(), and configureSession().
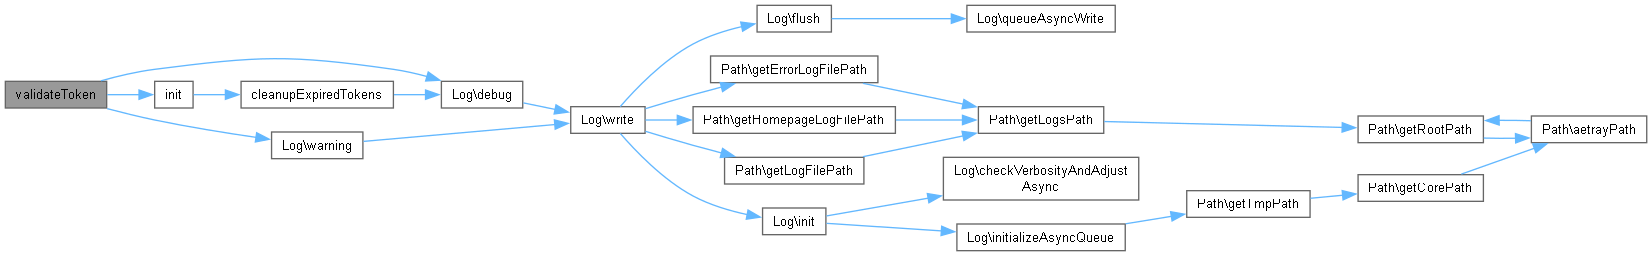
Referenced by generateToken(), getStats(), getToken(), regenerateToken(), and validateToken().
|
staticprivate |
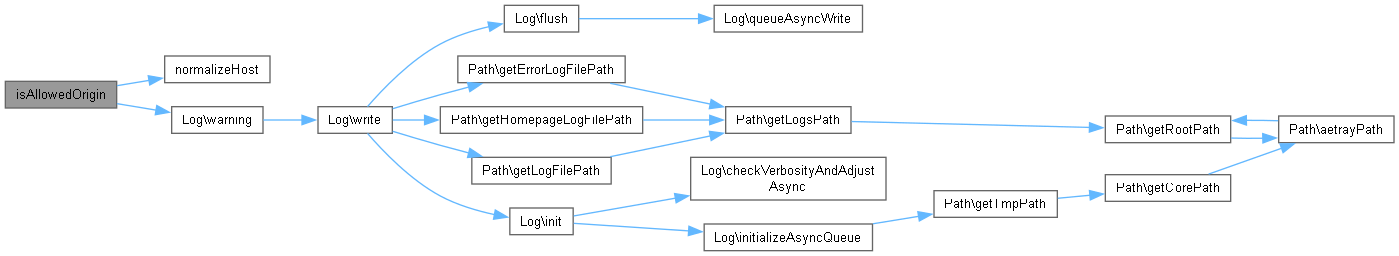
Checks that an Origin/Referer URL belongs to an allowed host and matches the scheme, host and effective port the request was addressed to.
| string | $url | The Origin or Referer header value. |
| string | $httpHost | The raw HTTP_HOST header (may include a port). |
| string | $scheme | The request scheme ('http' or 'https'). |
| array | $allowedHosts | The allowlist of permitted hosts. |
Definition at line 475 of file class.csrf.php.
References normalizeHost(), and Log\warning().
Referenced by validateOrigin().
|
staticprivate |
Checks whether a host is allowed, either by exact match against the allowlist or as a subdomain of an allowed wildcard host (e.g. www.vhost.local matches *.vhost.local). Wildcards mirror the certificate coverage BearSampp generates for virtual hosts.
| string | $host | The raw host to check. |
| array | $allowedHosts | The allowlist of normalized hosts and wildcards. |
Definition at line 414 of file class.csrf.php.
References normalizeHost().
|
staticprivate |
Normalizes a host header/name to a comparable form: lowercased, with any explicit port removed and IPv6 addresses bracketed ([::1]).
| string | $host | The raw host. |
Definition at line 445 of file class.csrf.php.
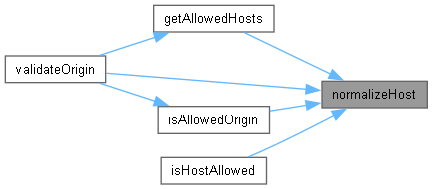
Referenced by getAllowedHosts(), isAllowedOrigin(), isHostAllowed(), and validateOrigin().
|
static |
Regenerates the CSRF token. Useful after sensitive operations or login.
Definition at line 635 of file class.csrf.php.
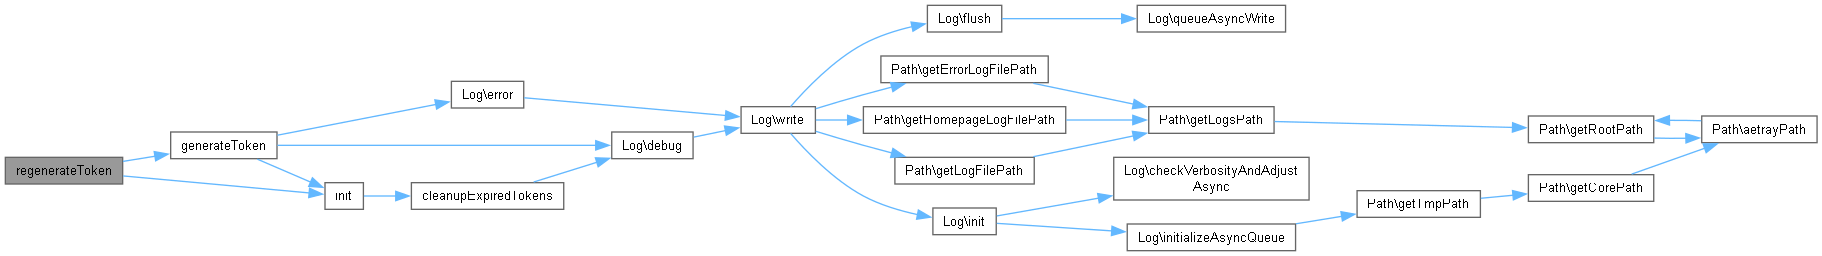
References generateToken(), and init().
|
static |
Validates request and sends JSON error response if validation fails. This is a convenience method for AJAX endpoints.
| bool | $removeAfterValidation | Whether to remove the token after successful validation |
Definition at line 679 of file class.csrf.php.
References exit.
|
staticprivate |
Validates that the request is addressed to an intended/trusted host and originates from that same origin.
The request host (HTTP_HOST) must be part of a fixed allowlist of hosts the local server is meant to serve (localhost, 127.0.0.1, ::1, the machine hostname and any configured virtual hosts). Comparing the Origin header against an attacker-influenced HTTP_HOST alone would not stop DNS-rebinding attacks, where a malicious domain is pointed at 127.0.0.1 and both the Host and Origin headers are controlled by the attacker.
Uses the Origin header when present and falls back to the Referer header. Browsers always send Origin on cross-origin POST requests, so a missing Origin/Referer on a state-changing request is treated as invalid.
Definition at line 266 of file class.csrf.php.
References getAllowedHosts(), isAllowedOrigin(), normalizeHost(), and Log\warning().
|
static |
Validates a CSRF token from the request (POST body or header). Checks $_POST['csrf_token'] first, then the X-CSRF-Token header. Also verifies the request is same-origin.
| bool | $removeAfterValidation | Whether to remove the token after successful validation |
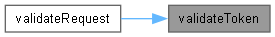
Definition at line 218 of file class.csrf.php.
References getAllHeaders(), validateToken(), and Log\warning().
|
static |
Validates a CSRF token.
| string | null | $token | The token to validate |
| bool | $removeAfterValidation | Whether to remove the token after successful validation (one-time use) |
Definition at line 171 of file class.csrf.php.
References Log\debug(), init(), and Log\warning().
Referenced by validateRequest().
| const MAX_TOKENS = 10 |
Maximum number of tokens to store per session This prevents session bloat from token accumulation
Definition at line 50 of file class.csrf.php.
| const SESSION_KEY = 'bearsampp_csrf_tokens' |
Session key for storing CSRF tokens
Definition at line 39 of file class.csrf.php.
| const TOKEN_EXPIRATION = 7200 |
Token expiration time in seconds (default: 2 hours)
Definition at line 44 of file class.csrf.php.
 1.17.0